CVE-2026-90843
What it is
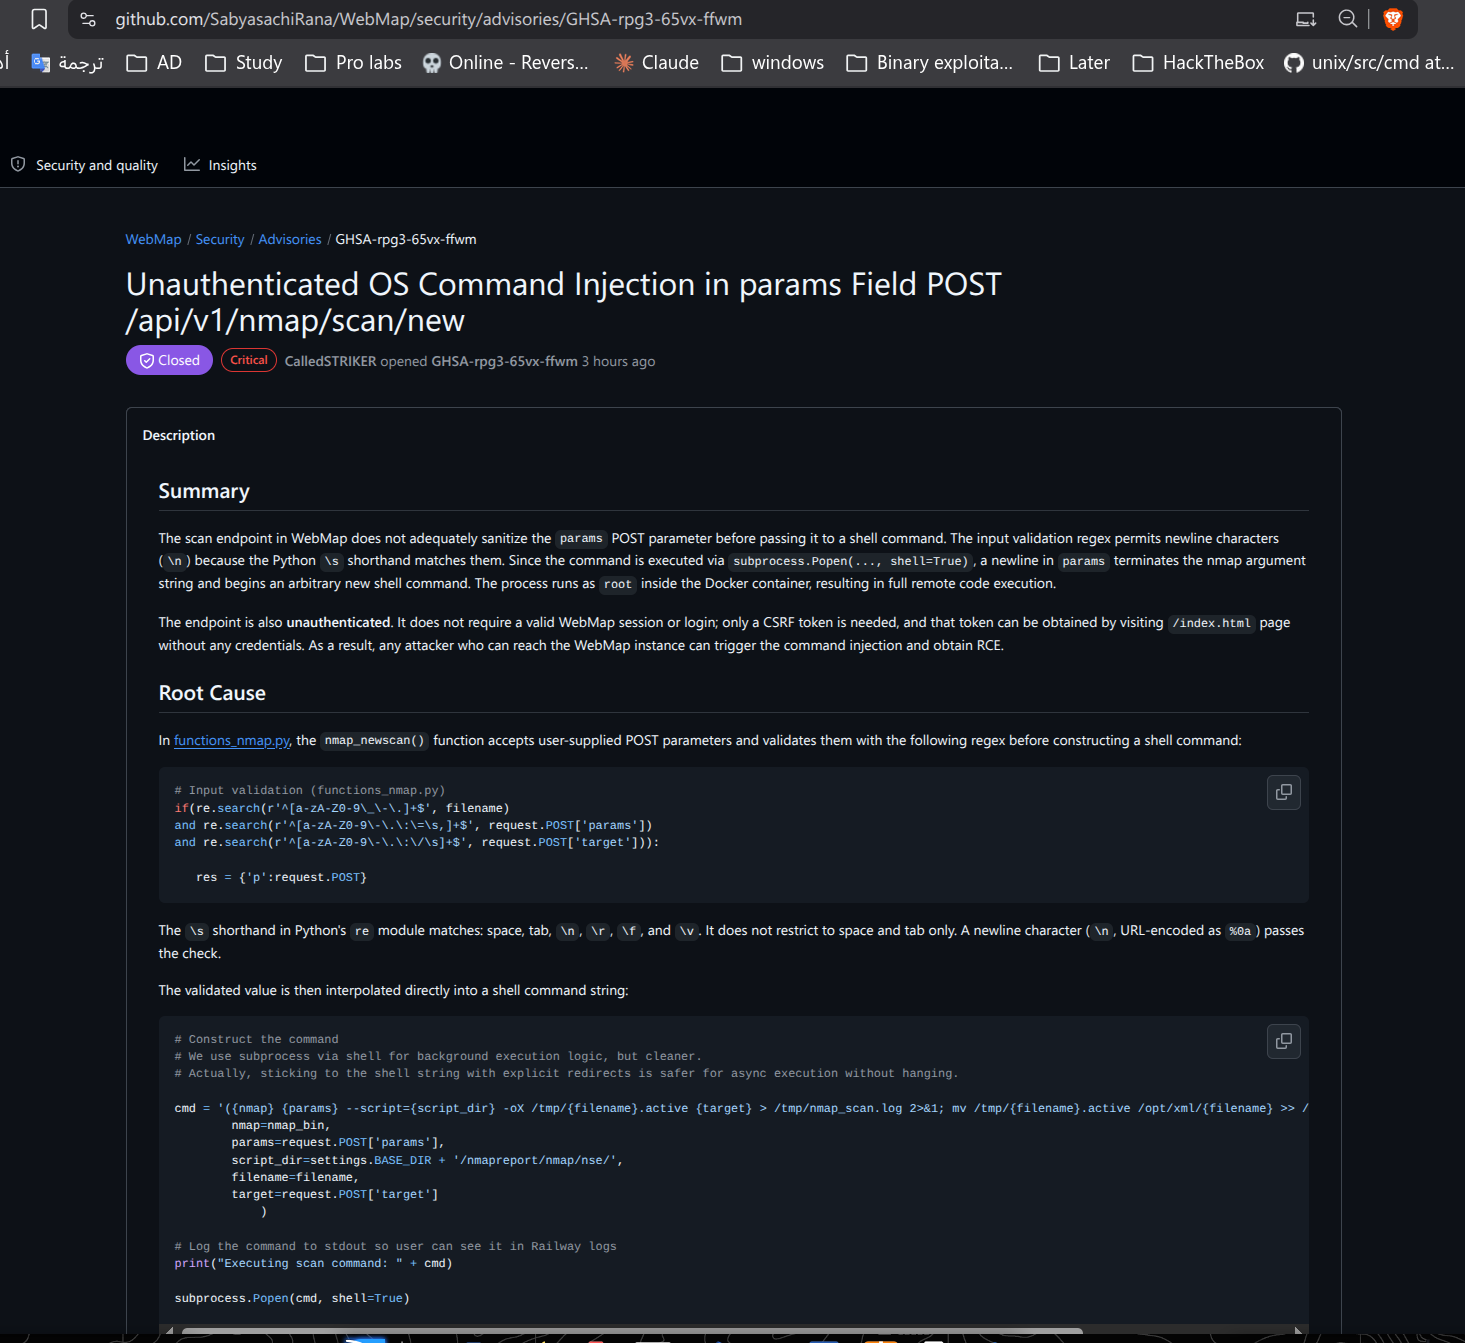
A security vulnerability has been detected in SabyasachiRana WebMap up to 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25. This affects the function nmap_newscan of the file functions_nmap.py of the component New Nmap Scan Handler. Such manipulation of the argument target/params leads to os command injection. The attack may be launched remotely. The exploit has been disclosed publicly and may be used. The name of the patch is 3d52f65803a2716bff14d938352c6fef45b0cfb6. A patch should be applied to remediate this issue. This issue got fixed with a silent patch.
At a glance
- Exploitability
- Can be exploited over the network without logging in. Limited direct impact.
- Exploit odds
- 2.2% chance of exploitation in the next 30 days (EPSS).
- Fix
- A patch, advisory or fixed version is referenced. Upgrade or apply it.
Timeline
- PublishedDisclosed publicly on CVE.org and NVD
- Last updatedMost recent change to the record
Why it ranks here
- Exploited in the wild: no, CISA does not list it.
- Exploit odds: 2.2% in the next 30 days (EPSS).
- Severity: 5.5 MEDIUM (CVSS).
- Fix: a patch or advisory is linked.
Details
- Published
- Last modified
- Exploit probability
- 2.2% · EPSS, next 30 days
- Weakness
- CWE-77 · Command injection
- Record status
- Deferred
Attack profile CVSS 4.0 · 5.5
- Attack vector
- Network
- Complexity
- Low
- Attack requirements
- None
- Privileges needed
- None
- User interaction
- None
- Confidentiality
- Low
- Integrity
- Low
- Availability
- Low
Raw vector
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:L/VA:L/SC:L/SI:L/SA:L/E:P/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X
Is it in your code?
Hand this to your coding agent. It searches your project for the affected products and checks versions. Nothing leaves your machine.
Read https://cve-list.com/agent/cve/CVE-2026-90843.md and follow it. Check whether this project is affected by CVE-2026-90843. Read only. Don't change anything and don't upload my code. Tell me yes, no or not sure, with the file as proof.


Fix and advisories
References
- https://calledstriker.gitbook.io/blog/security-research/webmap
- https://github.com/SabyasachiRana/WebMap/
- https://github.com/SabyasachiRana/WebMap/commit/3d52f65803a2716bff14d938352c6fef45b0cfb6
- https://raw.githubusercontent.com/CalledSTRIKER/CalledSTRIKER-gitbook/refs/heads/main/security-research/2026-05-30_12-29.png
- https://vuldb.com/cve/CVE-2026-90843
- https://vuldb.com/submit/925586
- https://vuldb.com/vuln/403395
- https://vuldb.com/vuln/403395/cti