CVE-2026-6743
What it is
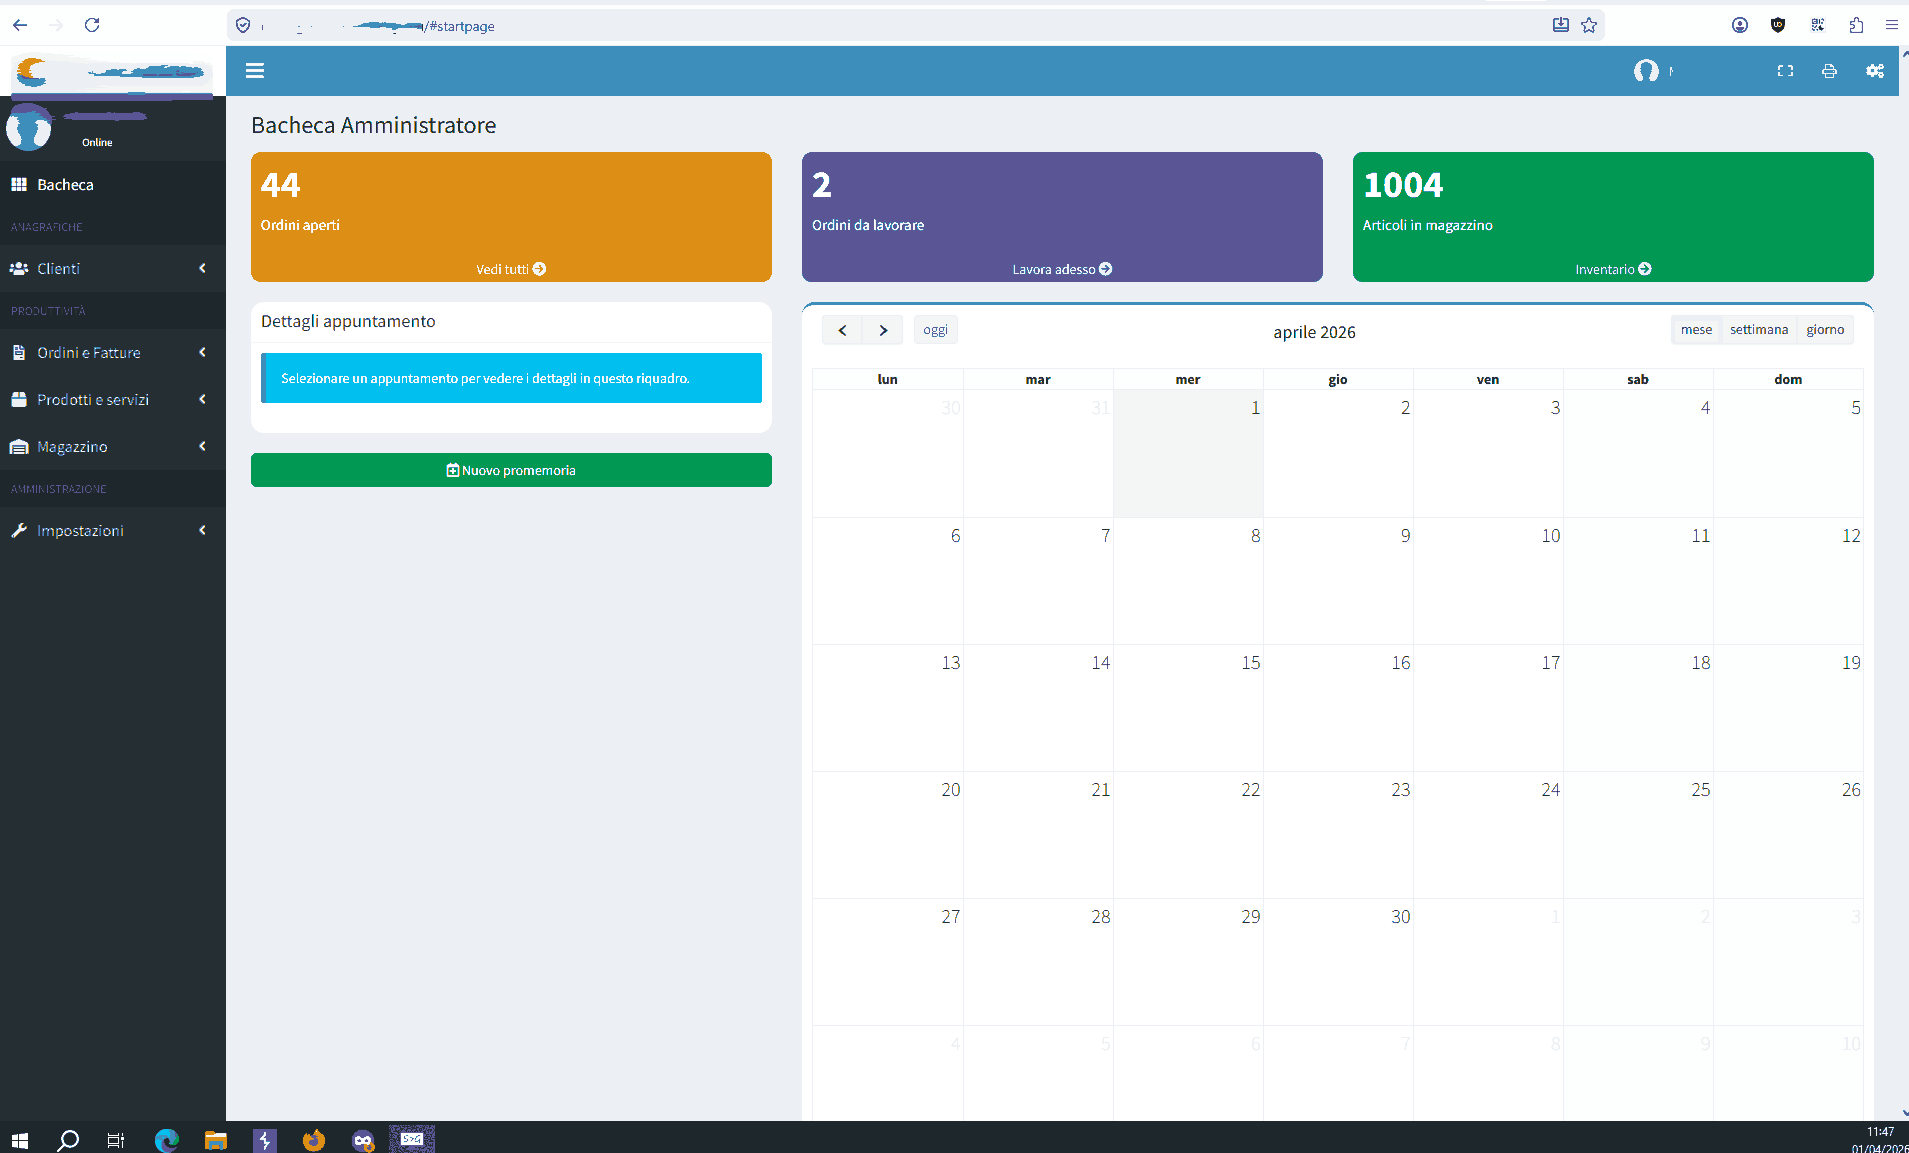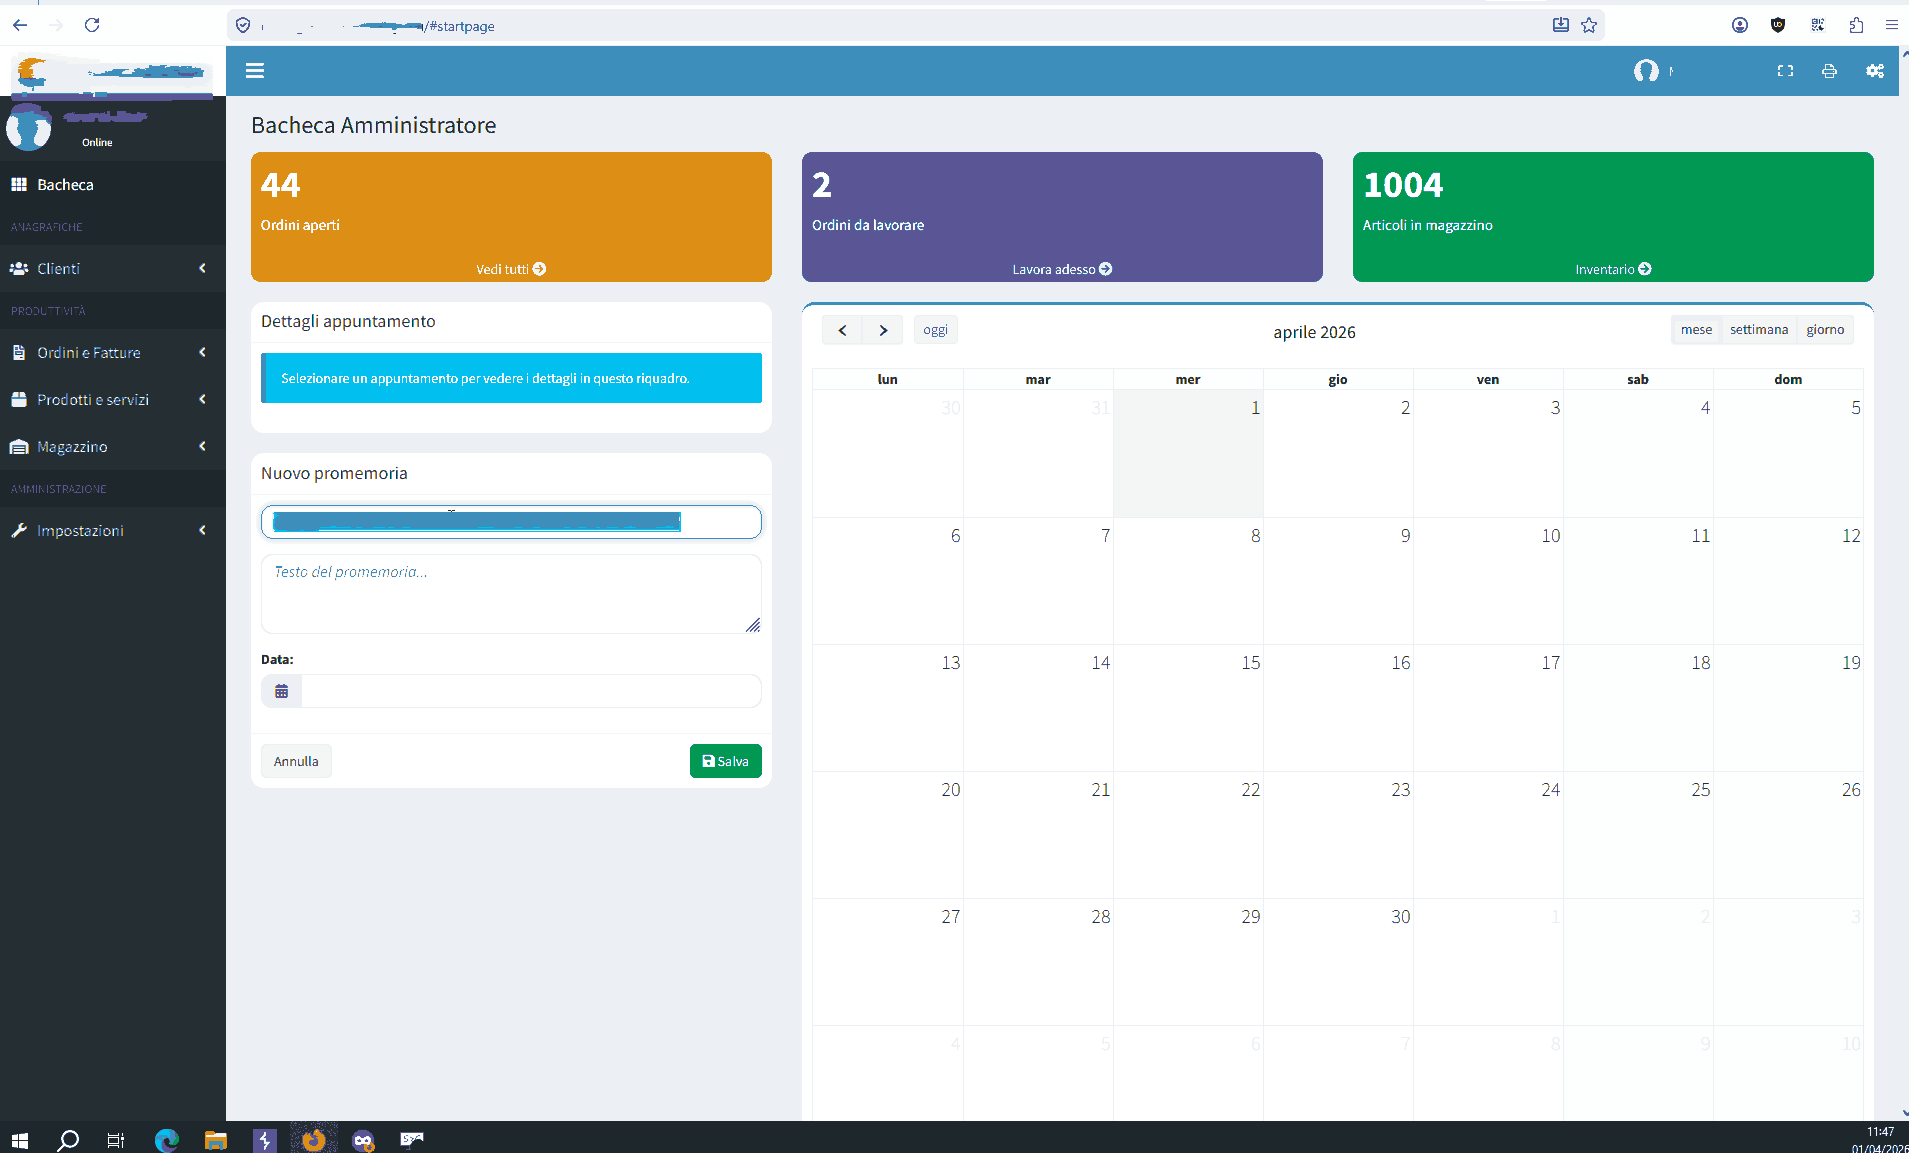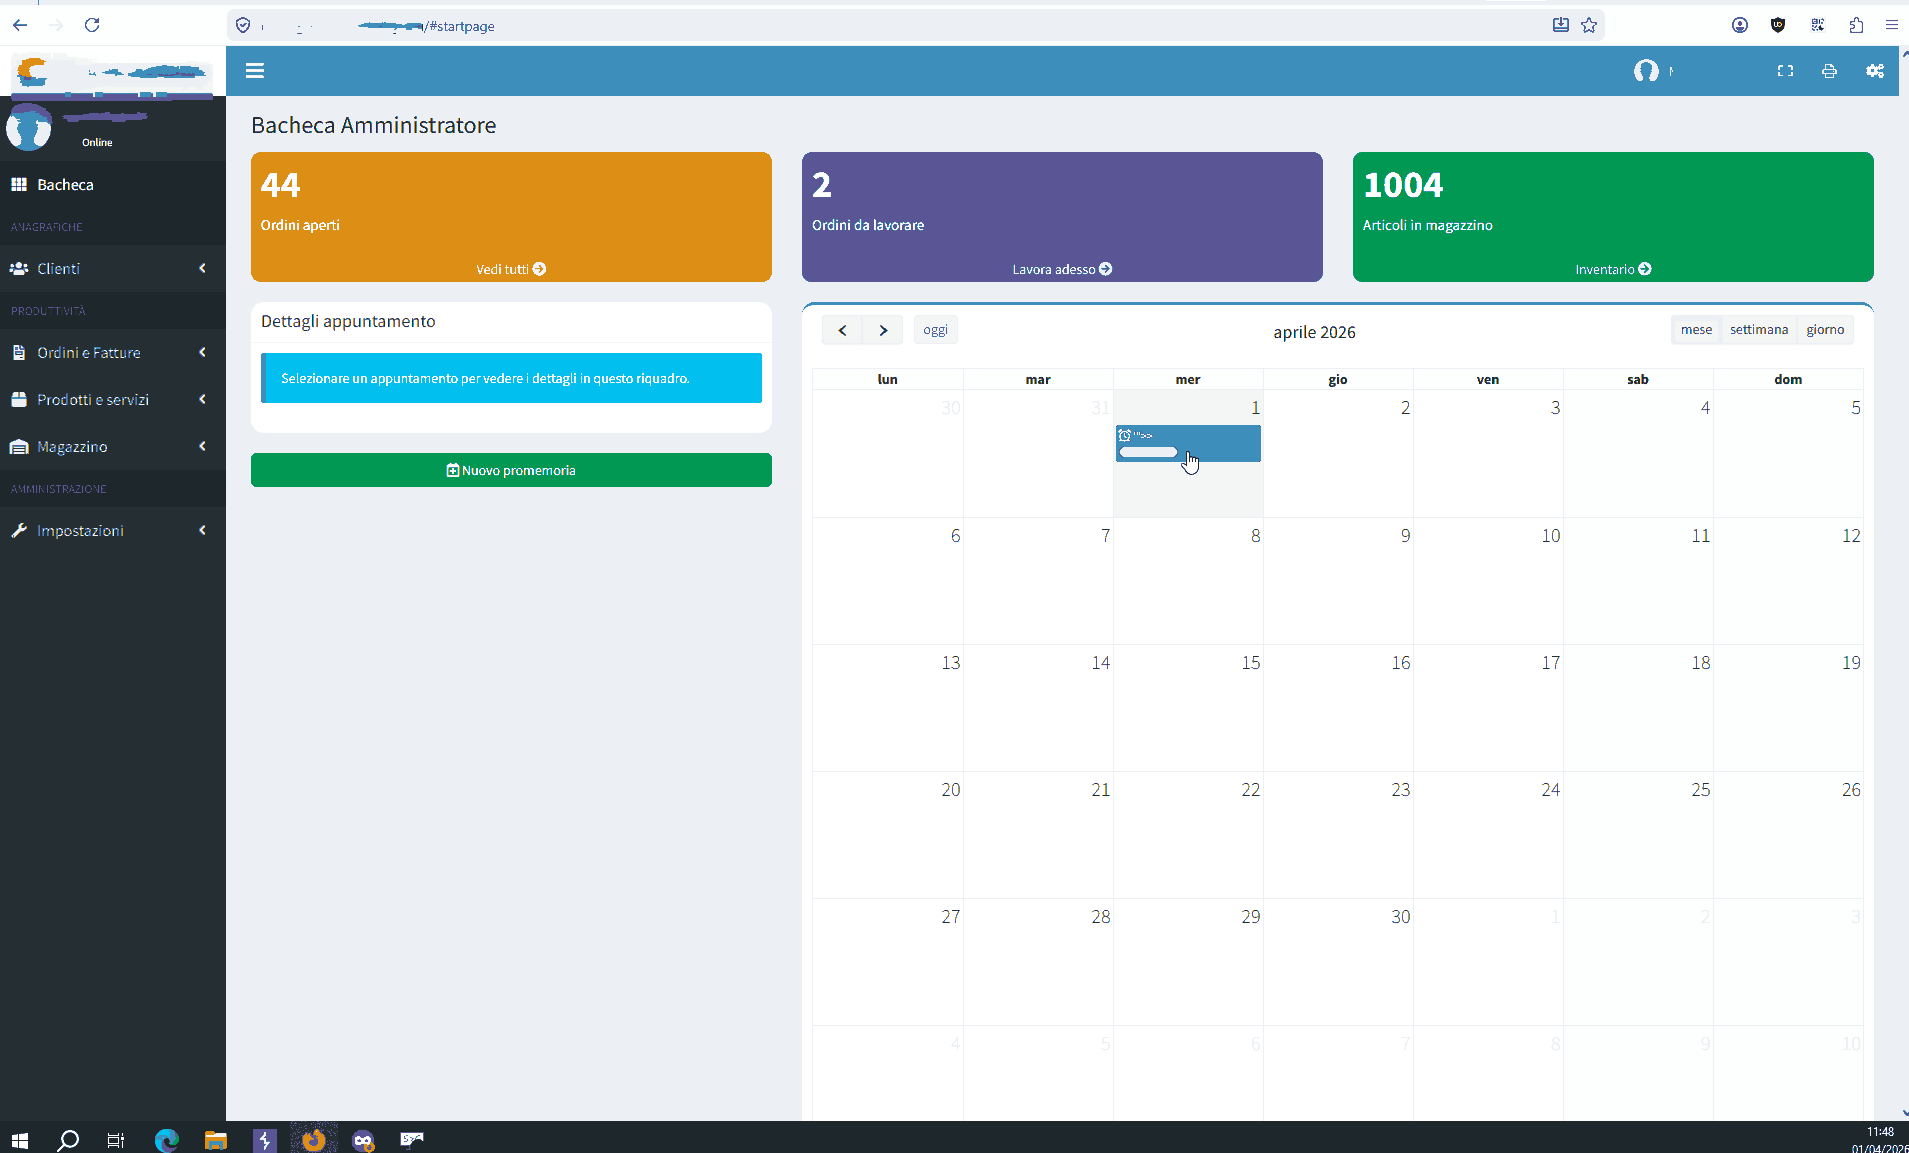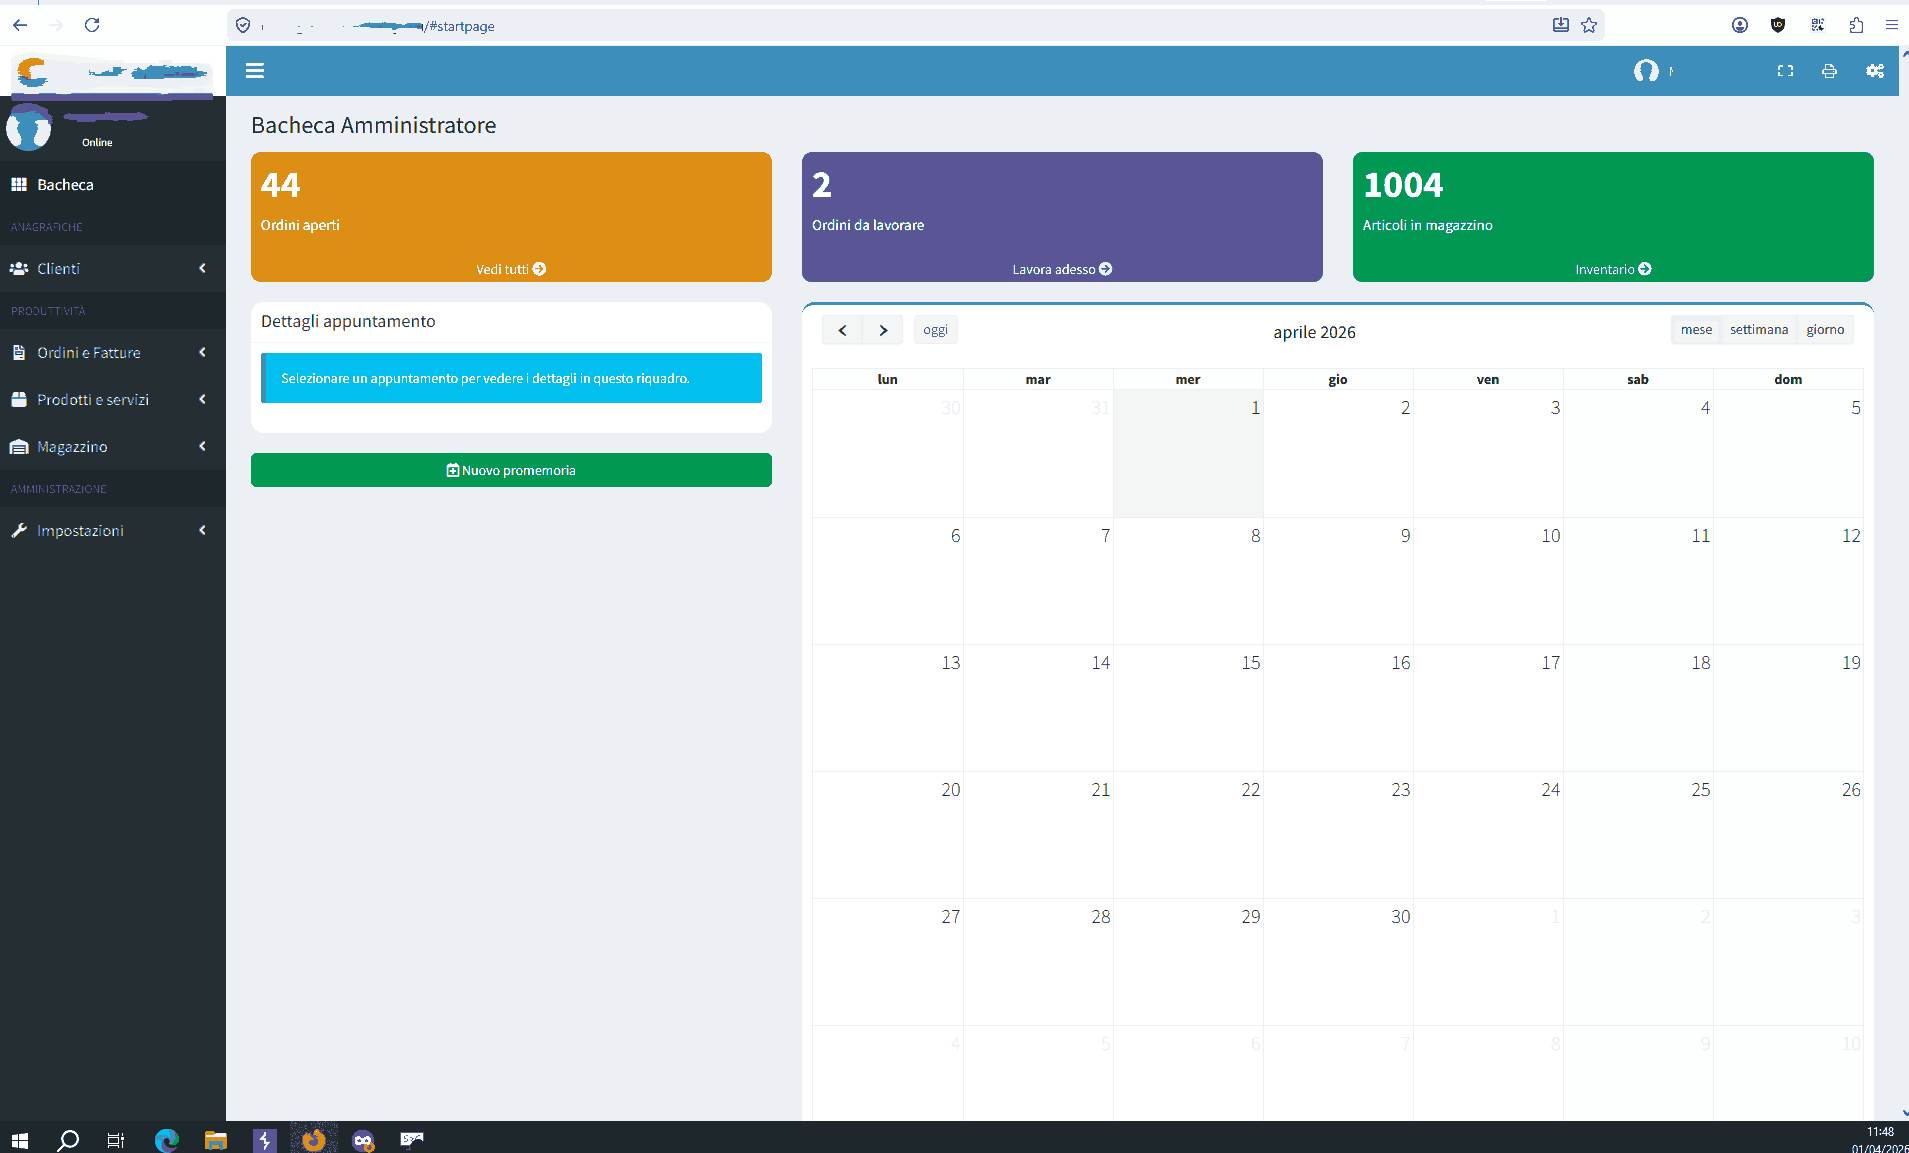
A vulnerability has been found in WebSystems WebTOTUM 2026. This impacts an unknown function of the component Calendar. The manipulation leads to cross site scripting. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. Upgrading the affected component is recommended. The vendor was contacted early, responded in a very professional manner and quickly released a fixed version of the affected product.
At a glance
- Exploitability
- Can be exploited over the network with a low-privilege account, but needs a user to act. Limited direct impact.
- Exploit odds
- 0.2% chance of exploitation in the next 30 days (EPSS).
- Fix
- No patch or advisory is linked yet. Look at mitigations or restrict exposure.
Timeline
- PublishedDisclosed publicly on CVE.org and NVD
- Last updatedMost recent change to the record
Details
- Published
- Last modified
- Exploit probability
- 0.2% · EPSS, next 30 days
- Weakness
- CWE-79 · Cross-site scripting
- Record status
- Deferred
Attack profile CVSS 4.0 · 2.0
- Attack vector
- Network
- Complexity
- Low
- Attack requirements
- None
- Privileges needed
- Low
- User interaction
- Passive
- Confidentiality
- None
- Integrity
- Low
- Availability
- None
Raw vector
CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:P/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N/E:P/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X