CVE-2024-26152
What it is
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 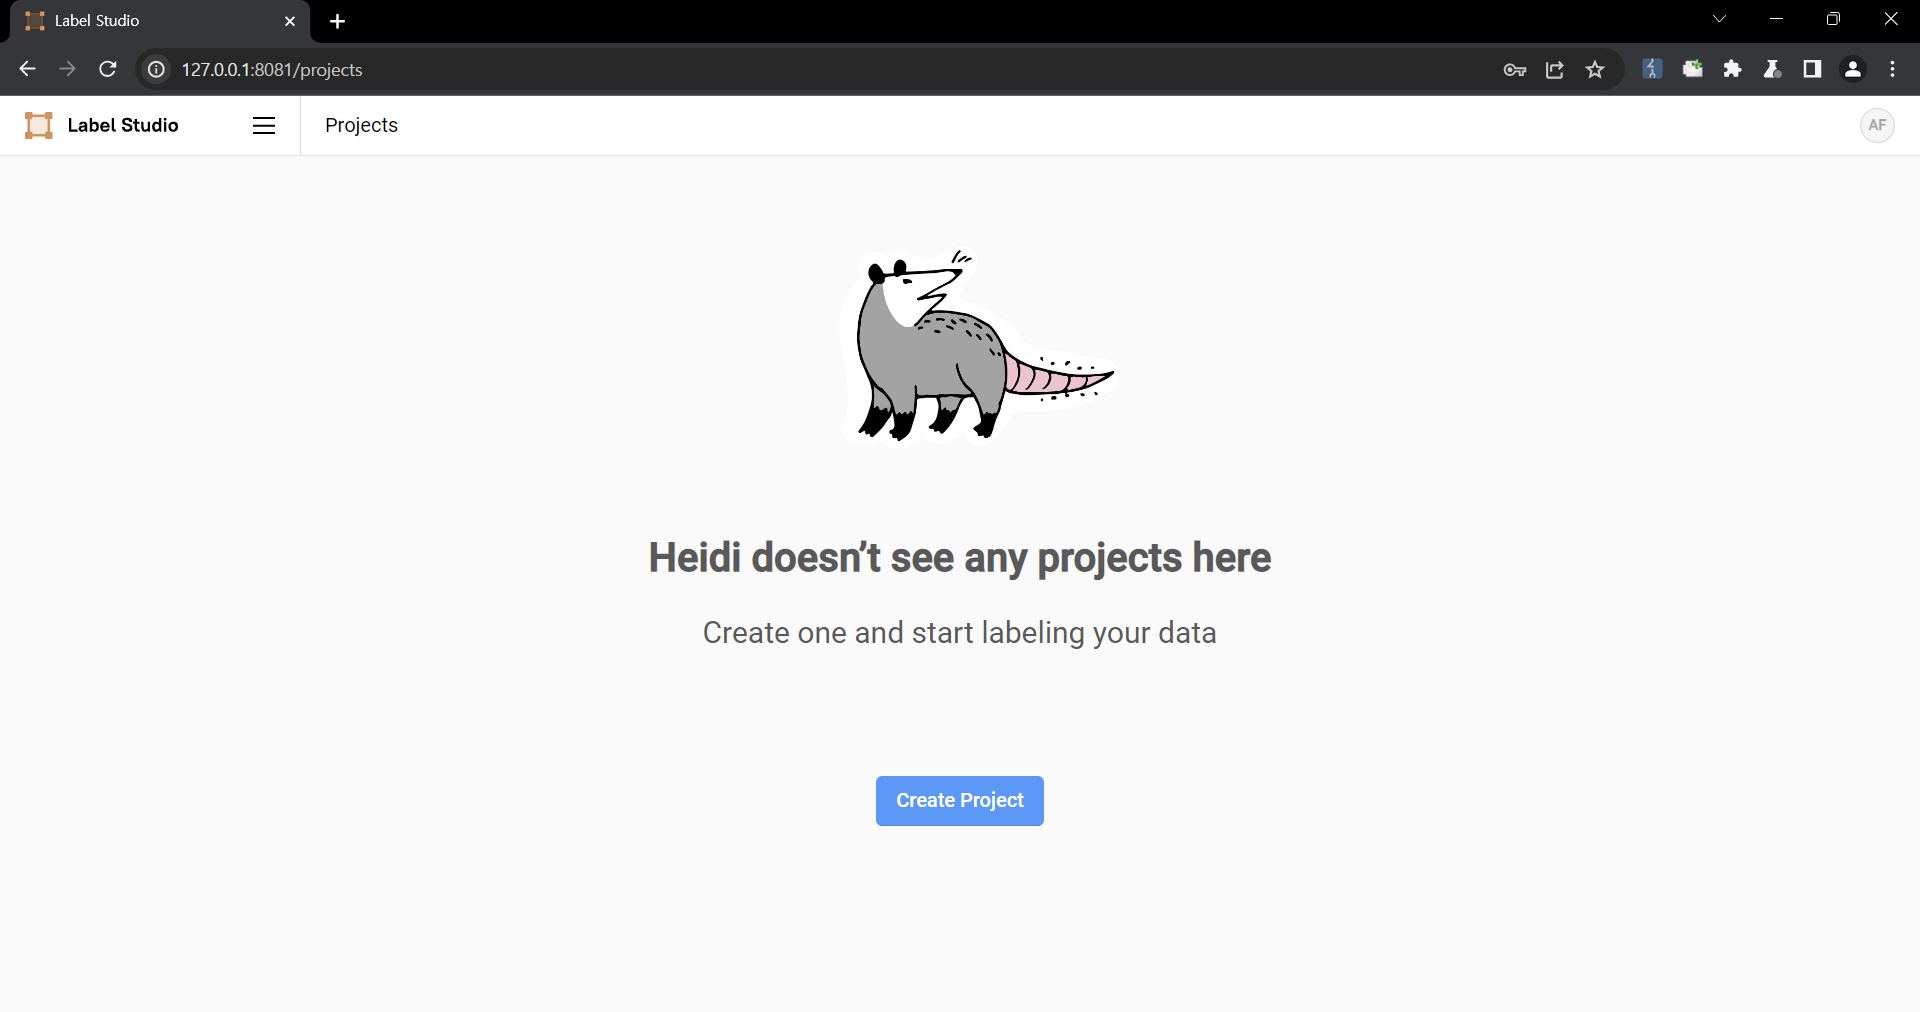 2. Upload a file containing the payload using the "Upload Files" function. 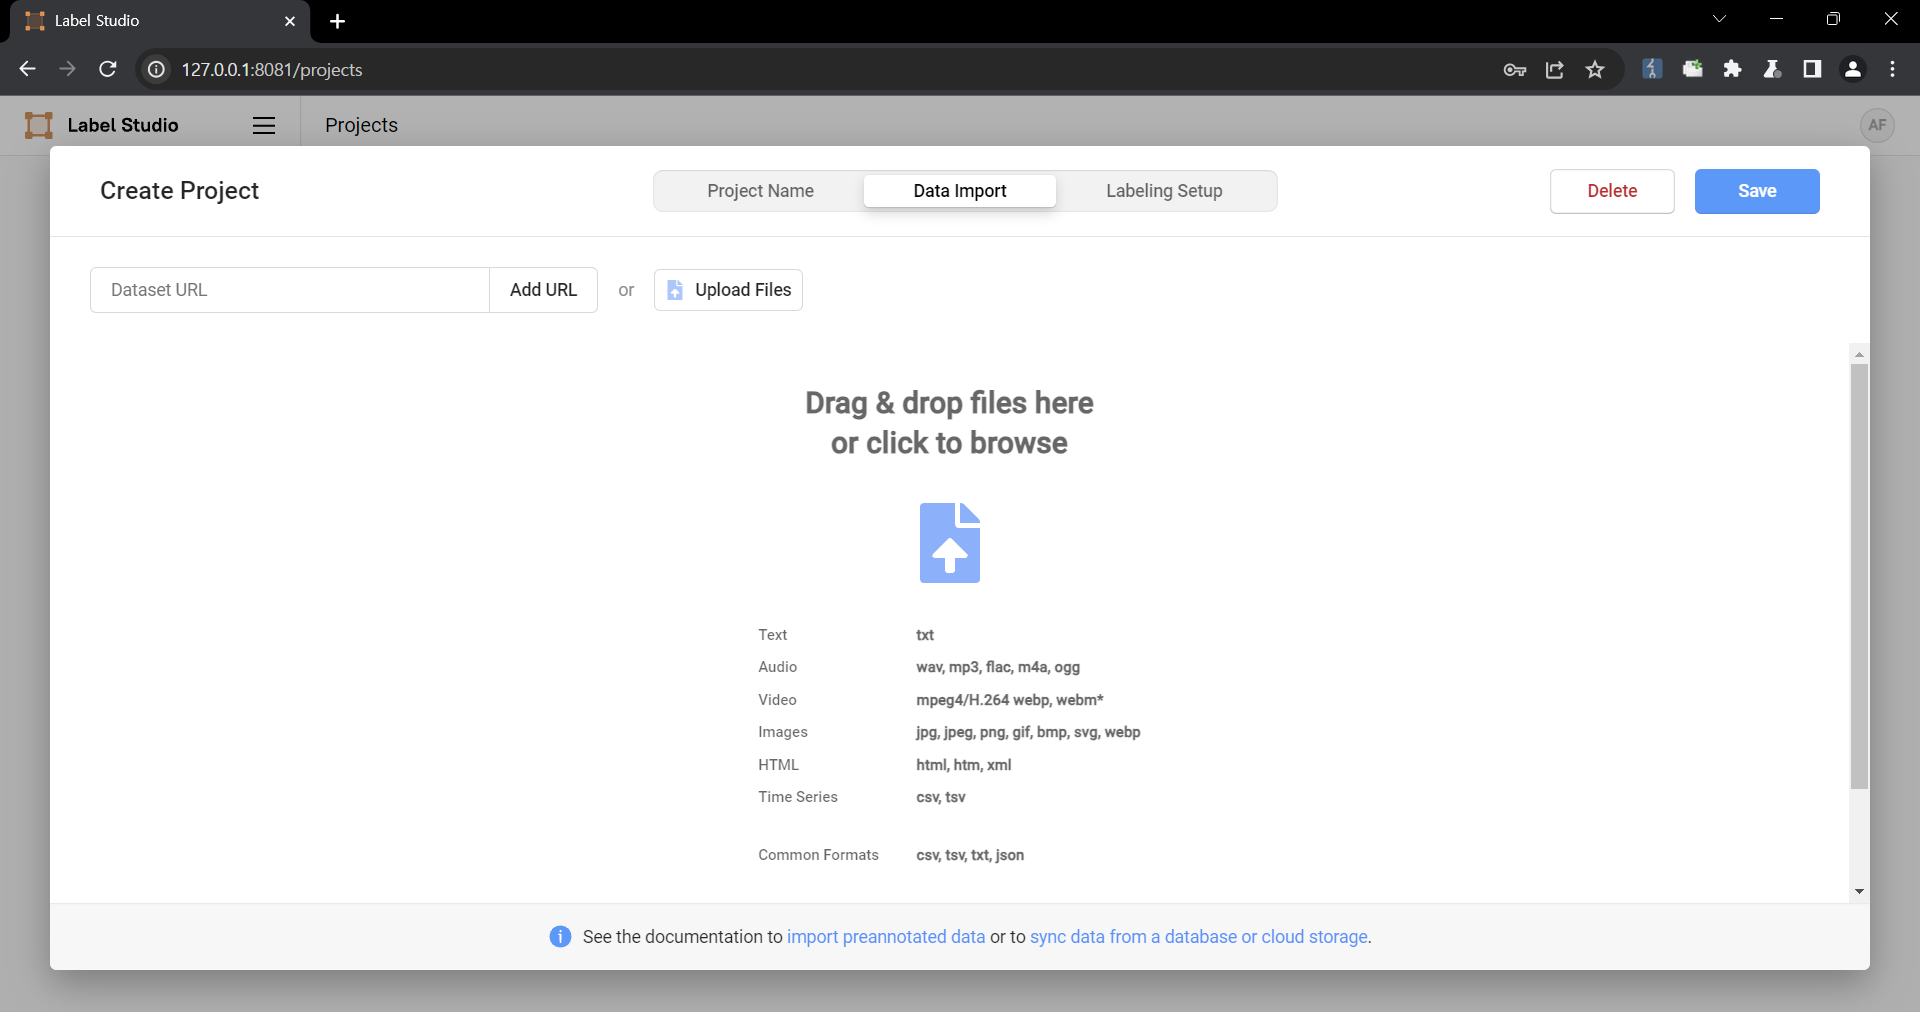 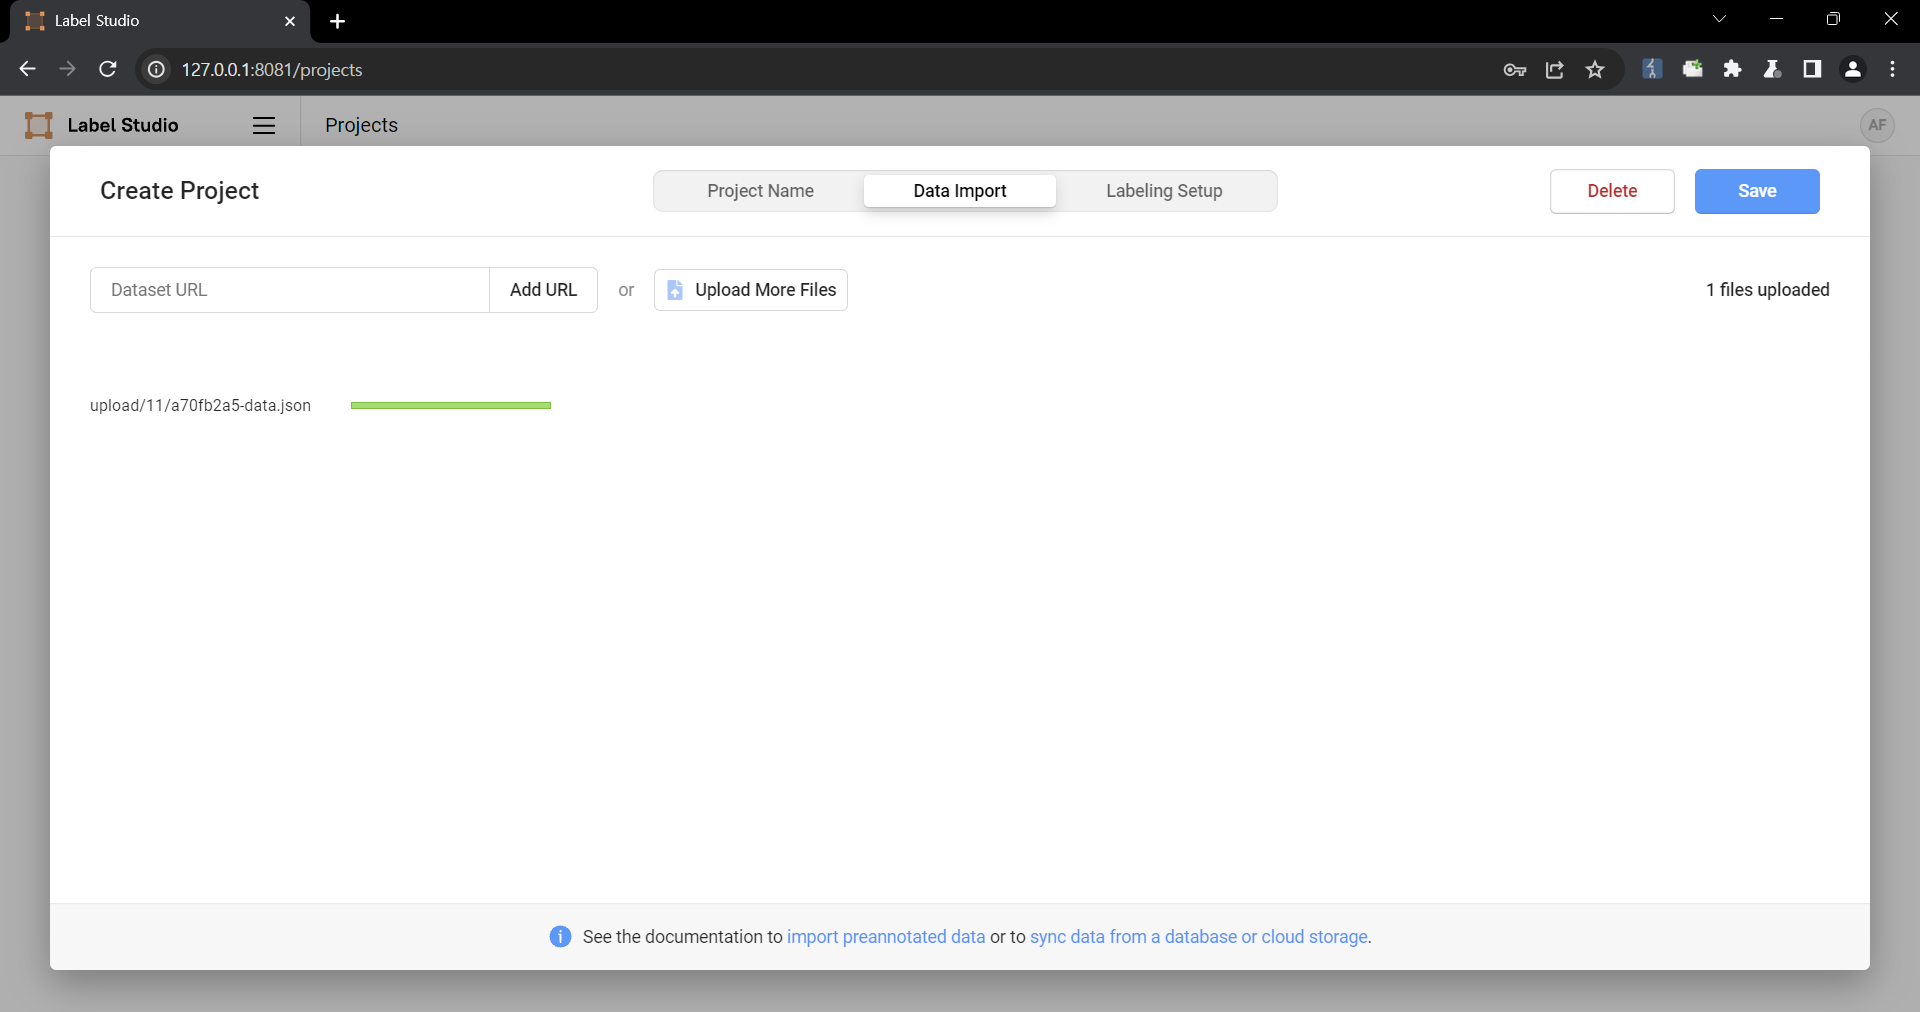 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring 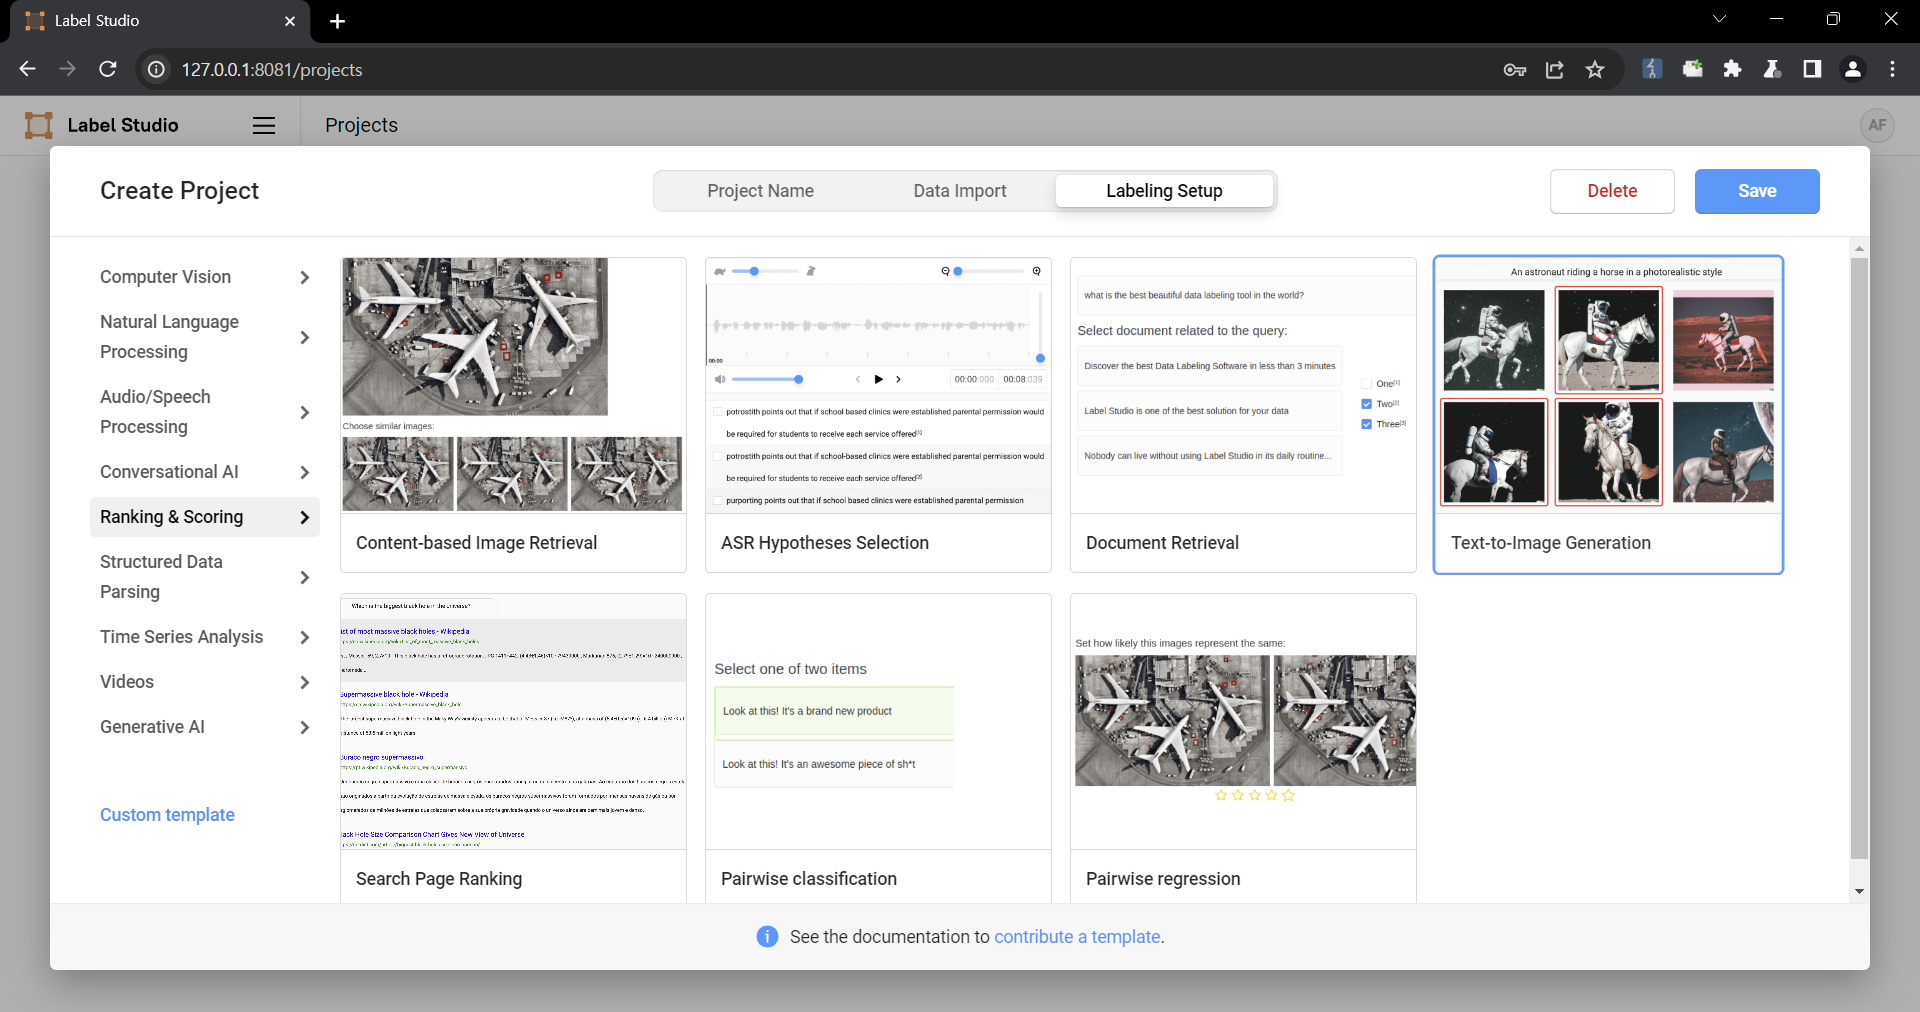 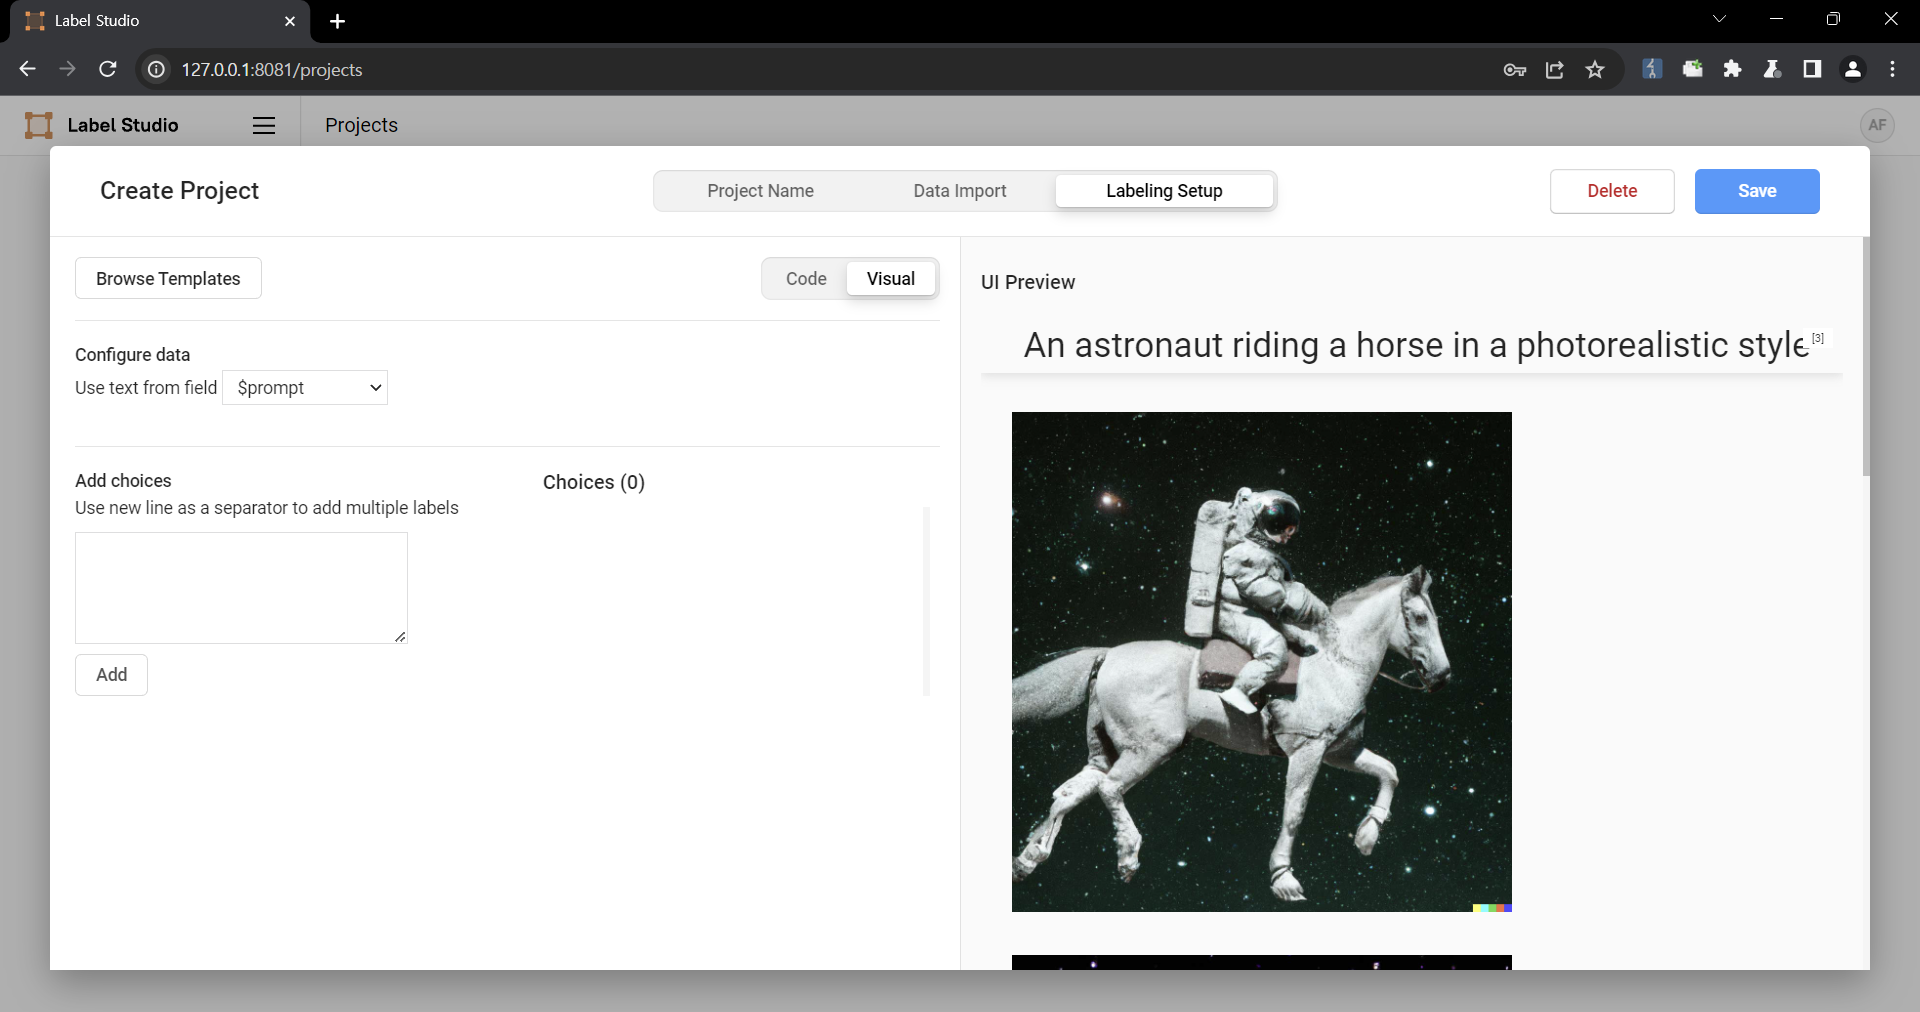 4. Select a task 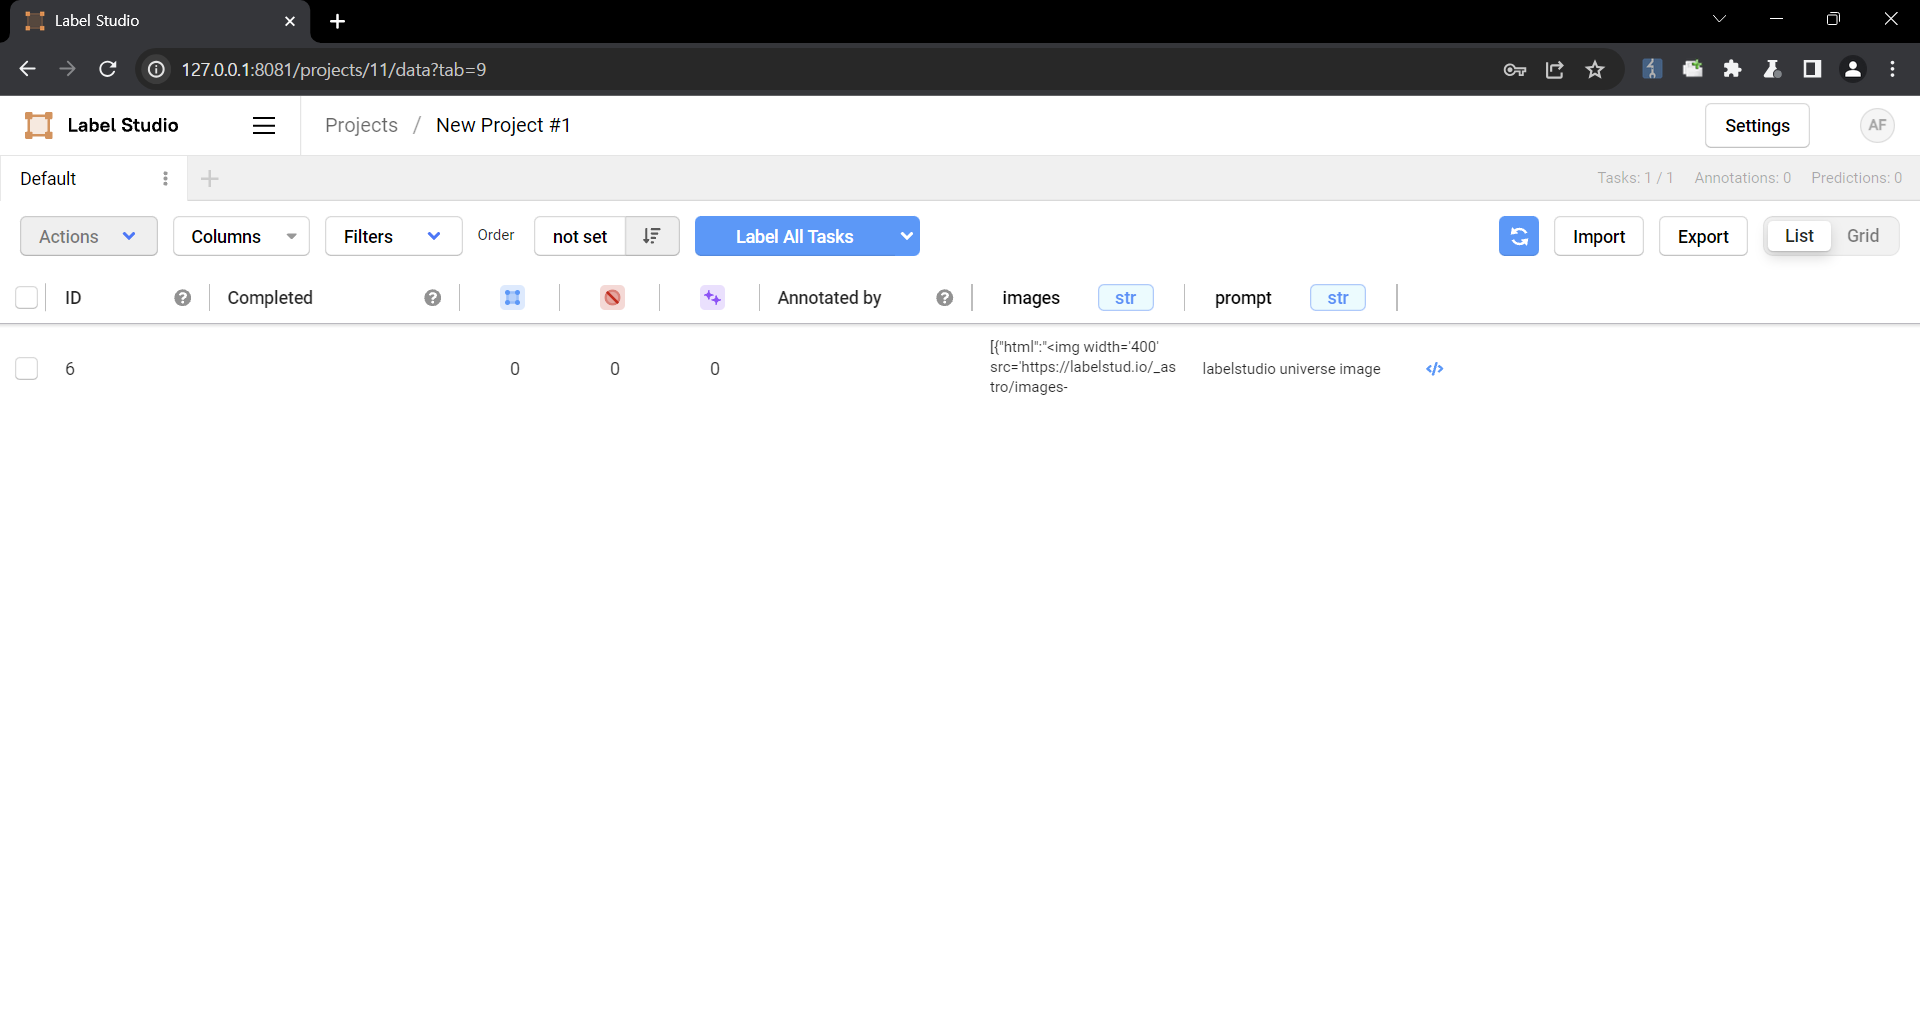 5. Check that the script is running 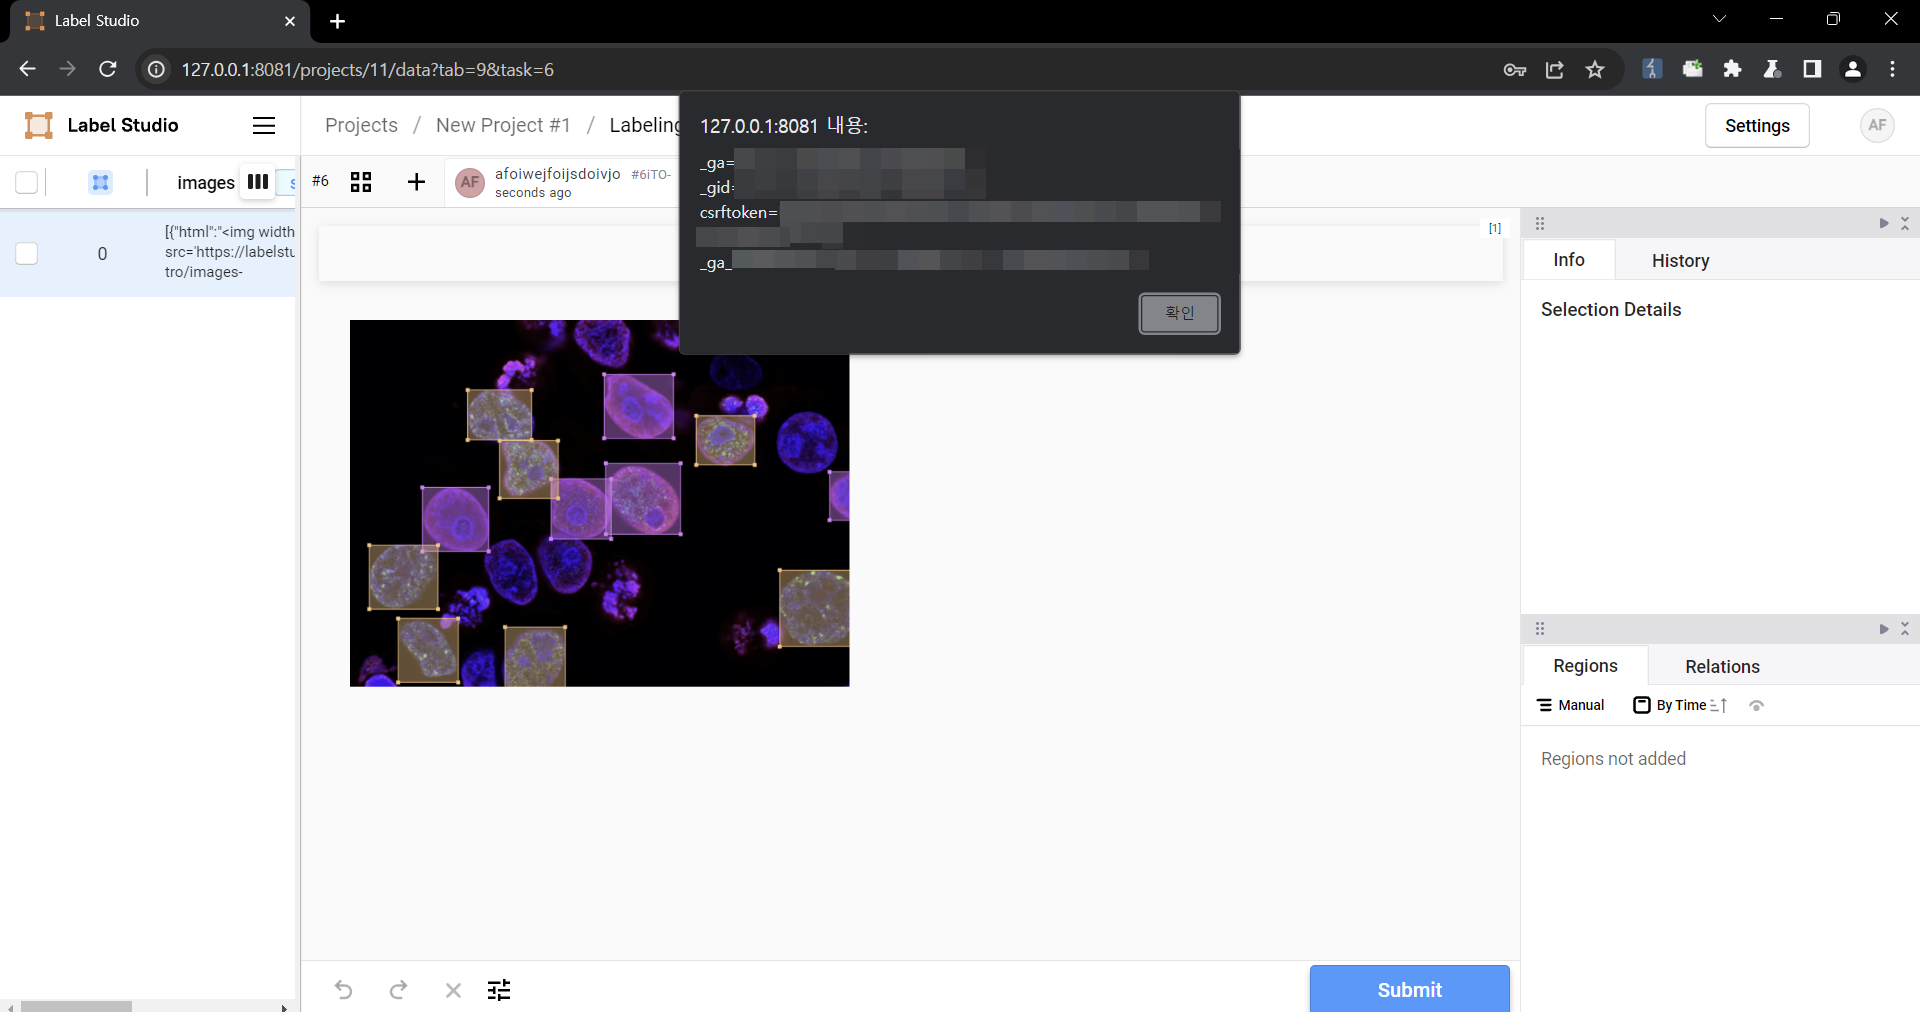 ### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
At a glance
- Exploitability
- Can be exploited over the network without logging in, but needs a user to act. Limited direct impact.
- Exploit odds
- 2.2% chance of exploitation in the next 30 days (EPSS).
- Fix
- A patch, advisory or fixed version is referenced. Upgrade or apply it.
Timeline
- PublishedDisclosed publicly on CVE.org and NVD
- Last updatedMost recent change to the record
Why it ranks here
- Exploited in the wild: no, CISA does not list it.
- Exploit odds: 2.2% in the next 30 days (EPSS).
- Severity: 4.7 MEDIUM (CVSS).
- Fix: a patch or advisory is linked.
Details
- Published
- Last modified
- Exploit probability
- 2.2% · EPSS, next 30 days
- Weakness
- CWE-79 · Cross-site scripting
- Record status
- Analyzed
Affected
- Humansignal Label Studio < 1.11.0
Attack profile CVSS 3.1 · 4.7
- Attack vector
- Network
- Complexity
- Low
- Privileges needed
- None
- User interaction
- Required
- Scope
- Changed
- Confidentiality
- Low
- Integrity
- None
- Availability
- None
Raw vector
CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N
Is it in your code?
Hand this to your coding agent. It searches your project for the affected products and checks versions. Nothing leaves your machine.
Read https://cve-list.com/agent/cve/CVE-2024-26152.md and follow it. Check whether this project is affected by CVE-2024-26152. Read only. Don't change anything and don't upload my code. Tell me yes, no or not sure, with the file as proof.


Fix and advisories
- https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8
- https://github.com/HumanSignal/label-studio/pull/5232
- https://github.com/HumanSignal/label-studio/releases/tag/1.11.0
- https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg
- https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8
- https://github.com/HumanSignal/label-studio/pull/5232
- https://github.com/HumanSignal/label-studio/releases/tag/1.11.0
- https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg
References
- https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8
- https://github.com/HumanSignal/label-studio/pull/5232
- https://github.com/HumanSignal/label-studio/releases/tag/1.11.0
- https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg
- https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8
- https://github.com/HumanSignal/label-studio/pull/5232
- https://github.com/HumanSignal/label-studio/releases/tag/1.11.0
- https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg