CVE-2018-19981
What it is
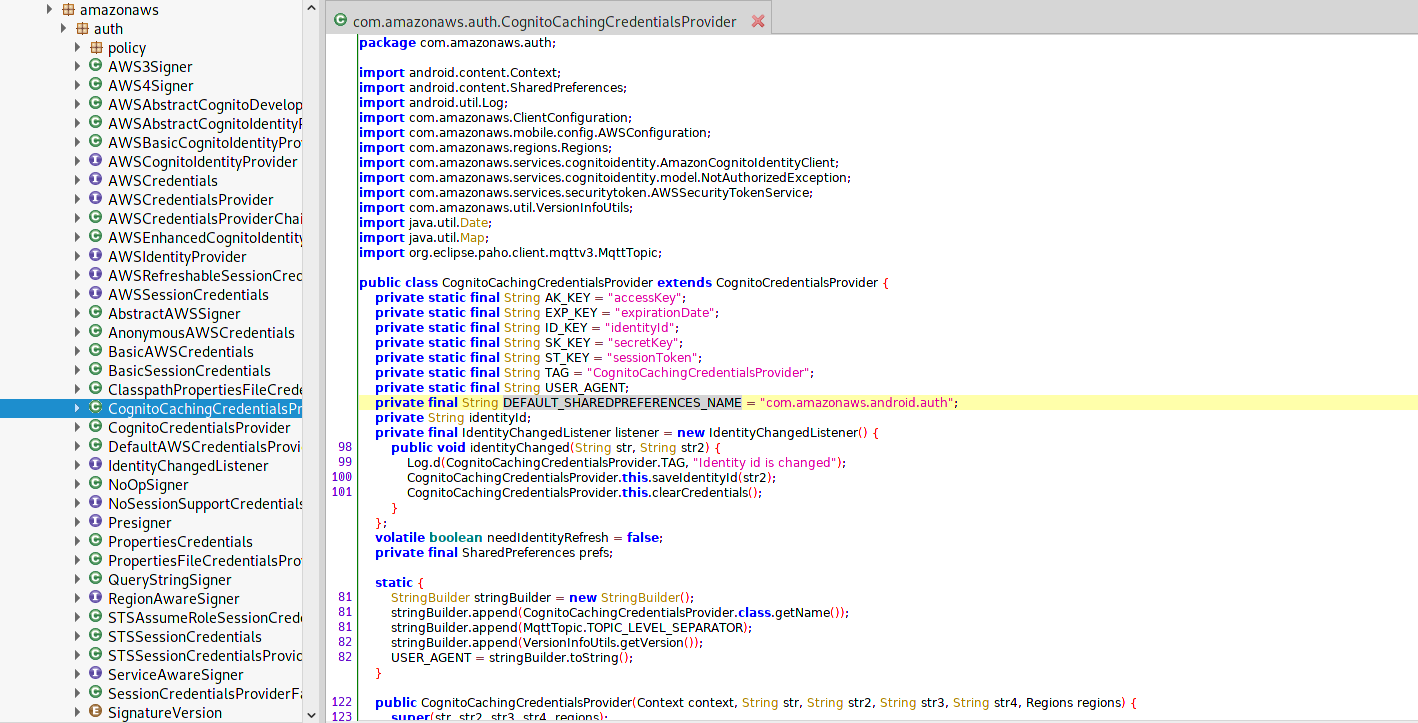
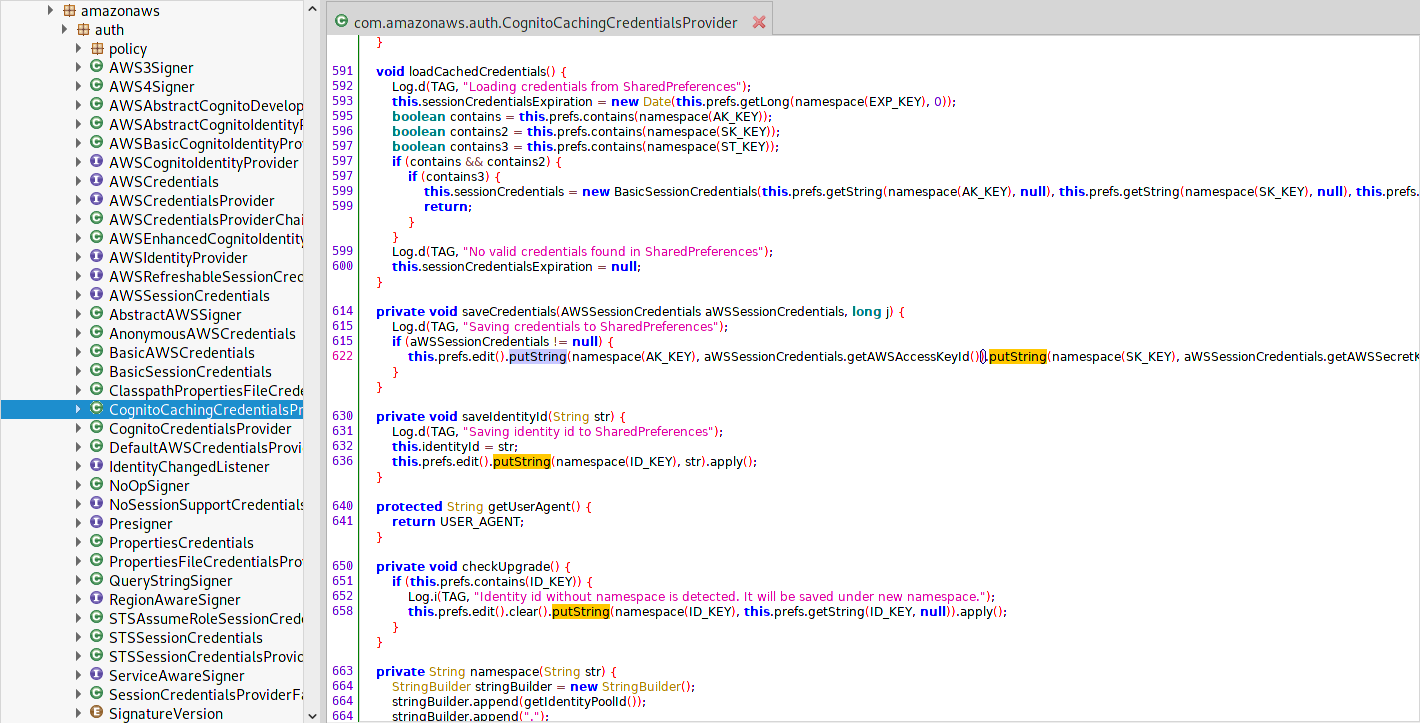
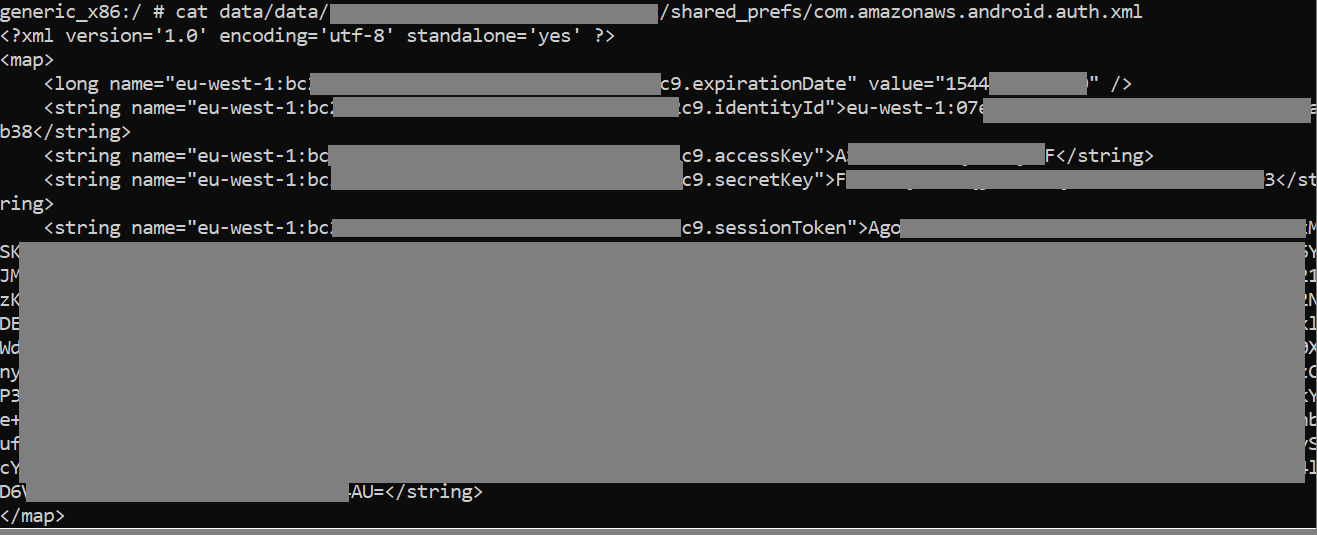
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS Temporary Credentials retrieved by AWS Cognito Identity Service. An attacker can use these credentials to create authenticated and/or authorized requests. Note that the attacker must have "root" privilege access to the Android filesystem in order to exploit this vulnerability (i.e. the device has been compromised, such as disabling or bypassing Android's fundamental security mechanisms).
At a glance
- Exploitability
- Can be exploited over the network with an admin-level account. High risk of data exposure, data tampering, service disruption.
- Exploit odds
- 1.8% chance of exploitation in the next 30 days (EPSS).
- Fix
- No patch or advisory is linked yet. Look at mitigations or restrict exposure.
Timeline
- PublishedDisclosed publicly on CVE.org and NVD
- Last updatedMost recent change to the record
Why it ranks here
- Exploited in the wild: no, CISA does not list it.
- Exploit odds: 1.8% in the next 30 days (EPSS).
- Severity: 7.2 HIGH (CVSS).
- Fix: none linked yet, which raises it.
Details
- Published
- Last modified
- Exploit probability
- 1.8% · EPSS, next 30 days
- Weakness
- CWE-312
- Record status
- Modified
Affected
- Amazon Aws Software Development Kit ≤ 2.8.5
Attack profile CVSS 3.0 · 7.2
- Attack vector
- Network
- Complexity
- Low
- Privileges needed
- High
- User interaction
- None
- Scope
- Unchanged
- Confidentiality
- High
- Integrity
- High
- Availability
- High
Raw vector
CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H
Is it in your code?
Hand this to your coding agent. It searches your project for the affected products and checks versions. Nothing leaves your machine.
Read https://cve-list.com/agent/cve/CVE-2018-19981.md and follow it. Check whether this project is affected by CVE-2018-19981. Read only. Don't change anything and don't upload my code. Tell me yes, no or not sure, with the file as proof.


References
- https://aws-amplify.github.io/aws-sdk-android/docs/reference/com/amazonaws/auth/CognitoCachingCredentialsProvider.html
- https://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_01.png
- https://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_02.png
- https://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_03.png
- https://aws-amplify.github.io/aws-sdk-android/docs/reference/com/amazonaws/auth/CognitoCachingCredentialsProvider.html
- https://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_01.png
- https://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_02.png
- https://raw.githubusercontent.com/lorenzodifuccia/cloudflare/master/Images/vulns/aws/aws_sdk_sp_03.png