CVE-2018-19461
What it is
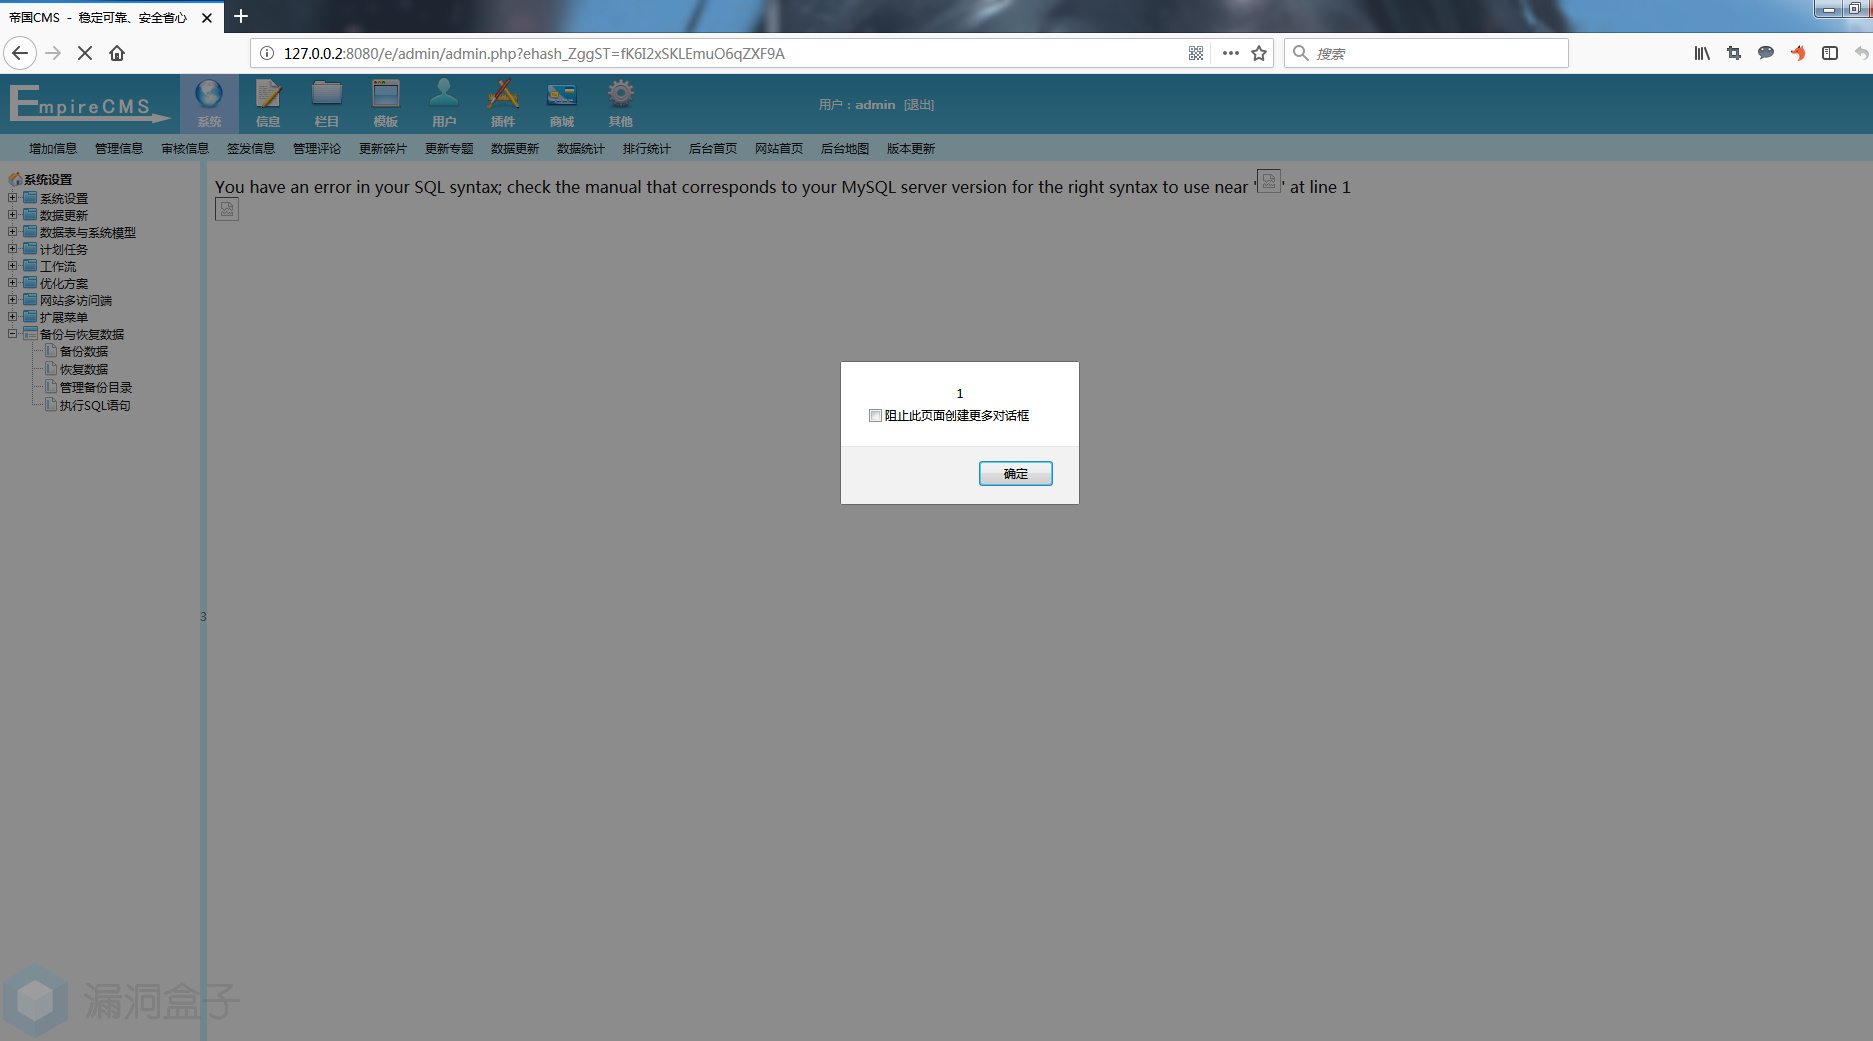
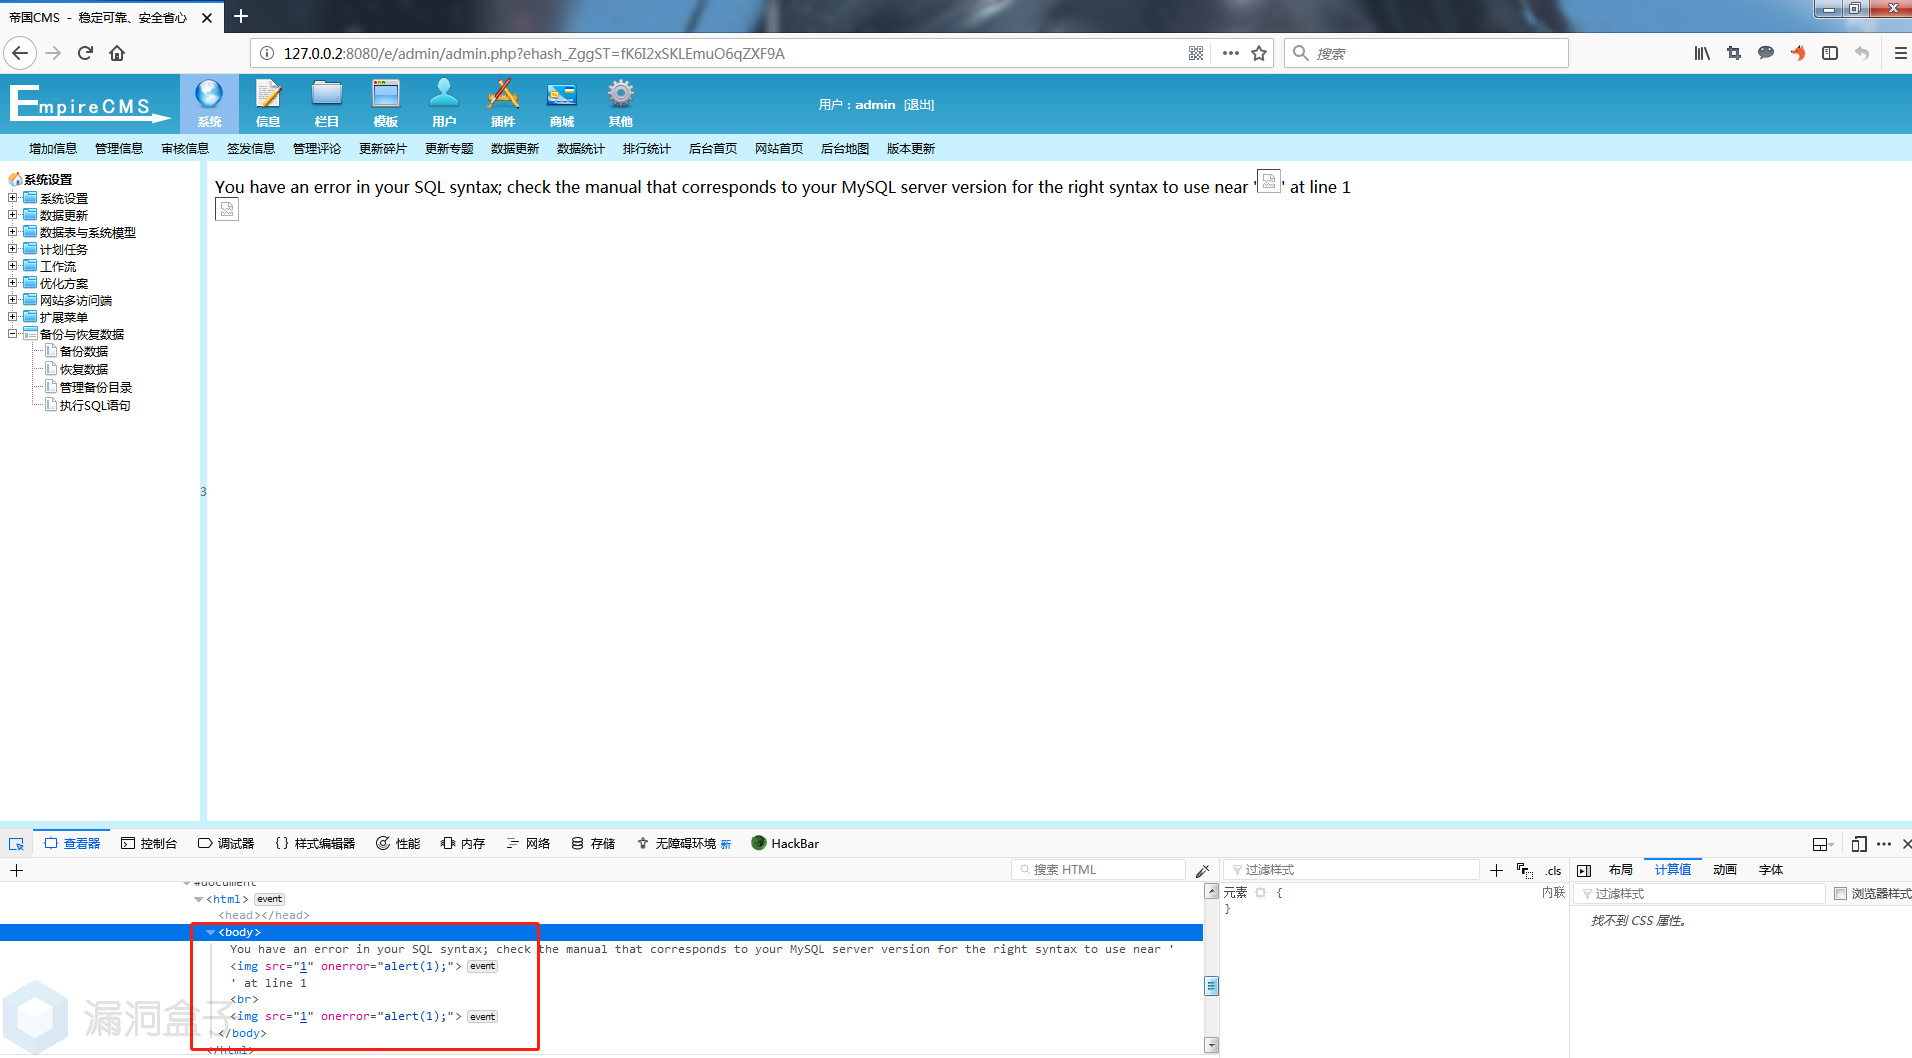
admin\db\DoSql.php in EmpireCMS through 7.5 allows XSS via crafted SQL syntax to admin/admin.php.
At a glance
- Exploitability
- Can be exploited over the network with an admin-level account, but needs a user to act. Limited direct impact.
- Exploit odds
- 0.9% chance of exploitation in the next 30 days (EPSS).
- Fix
- No patch or advisory is linked yet. Look at mitigations or restrict exposure.
Timeline
- PublishedDisclosed publicly on CVE.org and NVD
- Last updatedMost recent change to the record
Why it ranks here
- Exploited in the wild: no, CISA does not list it.
- Exploit odds: 0.9% in the next 30 days (EPSS).
- Severity: 4.8 MEDIUM (CVSS).
- Fix: none linked yet, which raises it.
Details
- Published
- Last modified
- Exploit probability
- 0.9% · EPSS, next 30 days
- Weakness
- CWE-79 · Cross-site scripting
- Record status
- Modified
Affected
- Phome Empirecms ≤ 7.5.0
Attack profile CVSS 3.0 · 4.8
- Attack vector
- Network
- Complexity
- Low
- Privileges needed
- High
- User interaction
- Required
- Scope
- Changed
- Confidentiality
- Low
- Integrity
- Low
- Availability
- None
Raw vector
CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:C/C:L/I:L/A:N
Is it in your code?
Hand this to your coding agent. It searches your project for the affected products and checks versions. Nothing leaves your machine.
Read https://cve-list.com/agent/cve/CVE-2018-19461.md and follow it. Check whether this project is affected by CVE-2018-19461. Read only. Don't change anything and don't upload my code. Tell me yes, no or not sure, with the file as proof.


References
- http://i.3001.net/uploads/Up_imgs/20181117-95a316d46f9a46dda7c48e541777d1fc.png%21small
- http://i.3001.net/uploads/Up_imgs/20181117-ce3d7d20372096011393bfda0d6f9d07.png%21small
- https://github.com/novysodope/empireCMS7.5
- http://i.3001.net/uploads/Up_imgs/20181117-95a316d46f9a46dda7c48e541777d1fc.png%21small
- http://i.3001.net/uploads/Up_imgs/20181117-ce3d7d20372096011393bfda0d6f9d07.png%21small
- https://github.com/novysodope/empireCMS7.5